A letter in the name of VR Bank Fulda
A fake letter with a QR code is circulating in the name of VR Bank Fulda eG. The letter is dated 14 October 2026 and carries the subject line "Confirmation of your business registration required". It is addressed to business customers and asks them to confirm their business data via a QR code. The letter is held by this newsroom and was analysed technically.
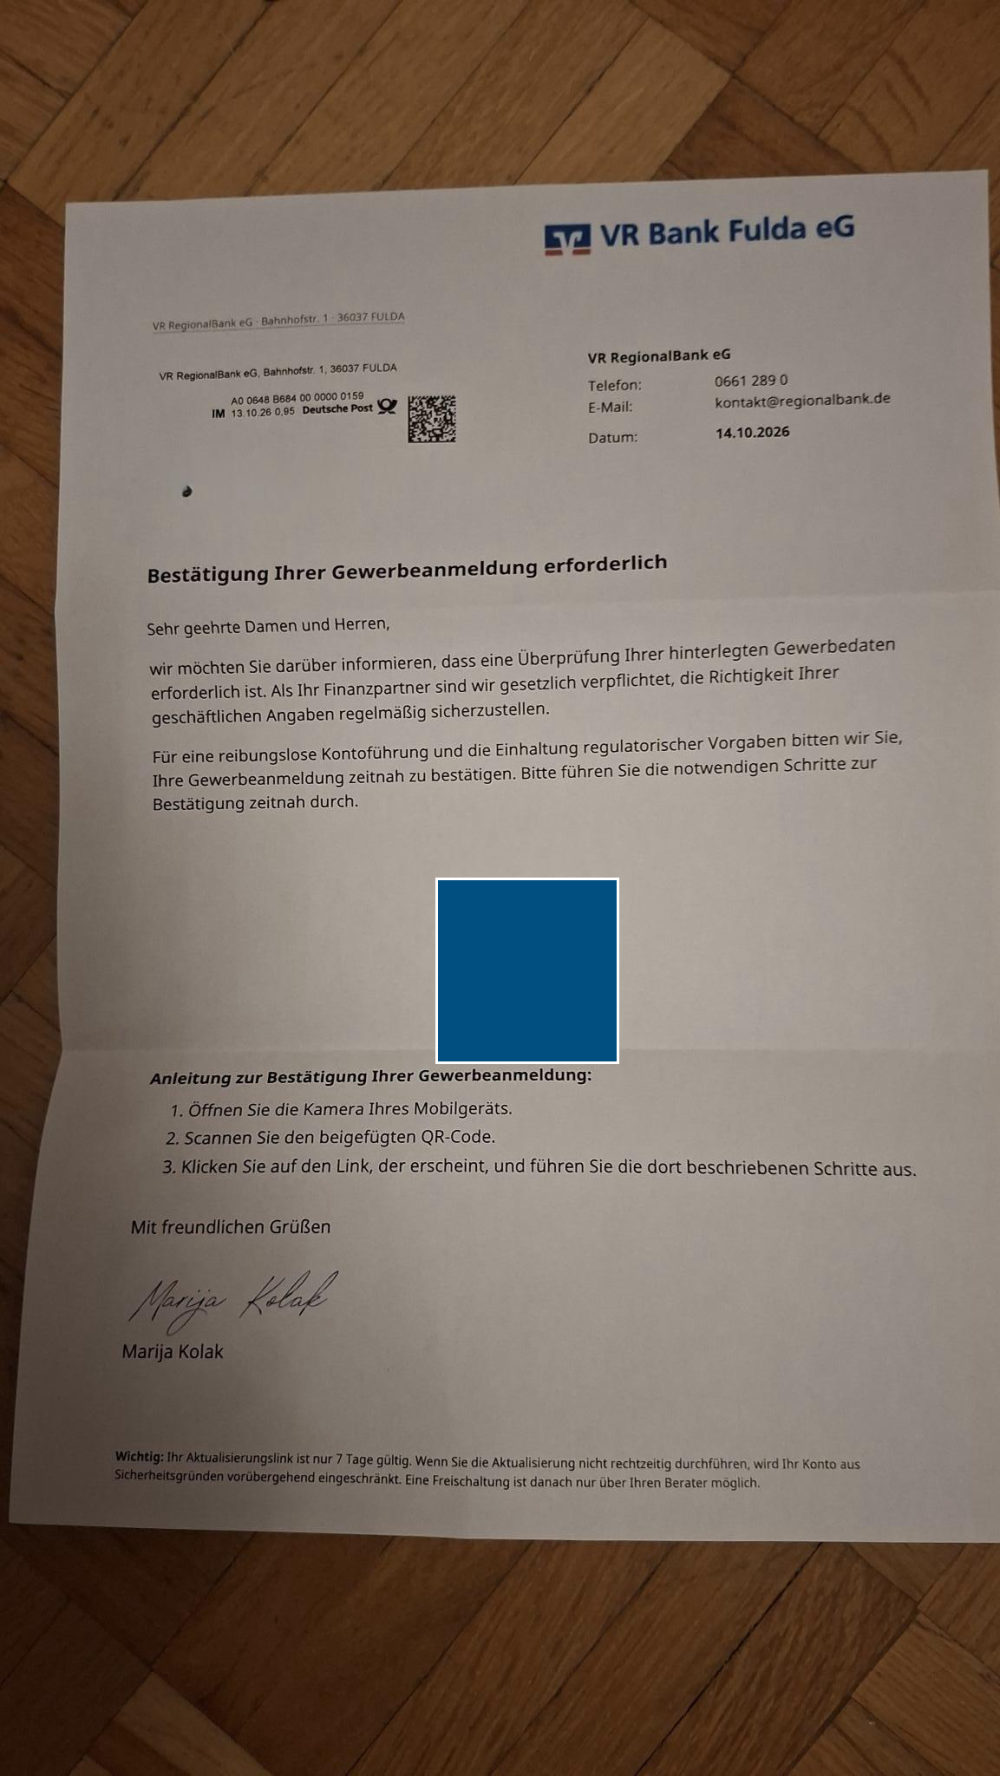
The fake letter in the name of VR Bank Fulda eG held by this newsroom. The QR code has been obscured to protect readers.
The letter names the sender as "VR RegionalBank eG, Bahnhofstraße 1, 36037 Fulda", with the contact address kontakt@regionalbank.de. It is signed in the name of Marija Kolak. Kolak is president of the national association of German cooperative banks (BVR) and does not sign on behalf of an individual bank. Her signature on the letter is forged.
Where the QR code leads
The QR code printed in the letter points to the domain deineupdateseite.com, reached via the subdomain vr.deineupdateseite.com. The domain was registered on 17 September 2026, around four weeks before the date on the letter. The registrar on record is a provider based in the Bahamas, and name resolution runs through DNSPod.
The page is served from a server in Riga, Latvia. It is titled "Sicherheitsverifizierung" (security verification) and reproduces the colours and look of the Volksbanken and Raiffeisenbanken online banking. The page source contains a reference to a request for a TAN. This allows not only login credentials but also the authorisation of individual transfers to be captured.
How to spot the fraud
- The letterhead names "VR Bank Fulda eG", the sender "VR RegionalBank eG"; the address kontakt@regionalbank.de belongs to no genuine bank domain.
- The letter is signed in the name of BVR president Marija Kolak, who does not sign for any single bank.
- The destination domain was registered only weeks before the mailing and anonymised through a foreign registrar.
- The letter applies time pressure: the link is said to be valid for only seven days, otherwise the account will be restricted.
Part of a nationwide scheme
The national association of German cooperative banks had already warned in mid-October that fake letters bearing the name Marija Kolak were circulating across Germany. A comparable case had emerged in Bottrop and Dorsten (report). The method is called quishing, a form of phishing in which the malicious link is hidden inside a QR code.
What recipients should look out for
- • Do not scan the QR code from an unexpected bank letter and do not follow its instructions.
- • Never enter login data or a TAN on a page you reached via a QR code from a letter.
- • Scrutinise the sender, especially when artificial time pressure is applied.
- • When in doubt, contact your bank directly, using the number on your bank card or statement.
- • If you have already scanned the code and entered data, inform your bank and have your access and cards blocked.
Check a QR code before opening it
QRTrust displays a QR code’s full destination address and checks it against multiple phishing databases and AI models before it opens, revealing where a QR code from a letter really leads.
Check a QR code →Sources
- Technical analysis of the letter and the destination URL by the QRTrust newsroom, 24 October 2026 (QR code, domain registration, hosting, page source).
- WAZ: „Zerreißen Sie den Brief" – Volksbank in Bottrop warnt vor neuer Betrugsmasche (20.10.2026)
About QRTrust
QRTrust is Germany's first QR code security platform, developed in Dortmund. AI-powered real-time detection, a local threat database and multi-layered security checks protect citizens, authorities and businesses from quishing attacks. GDPR compliant, hosted in Germany.